Cybersecurity made practical.
Our Vision
To make practical cybersecurity accessible to small and growing businesses, helping them operate securely, confidently and resiliently in a digital world.
Our Mission
To help businesses understand their cybersecurity risks and take practical action to protect their people, systems and data through security assessments, risk-focused solutions, security services and education.
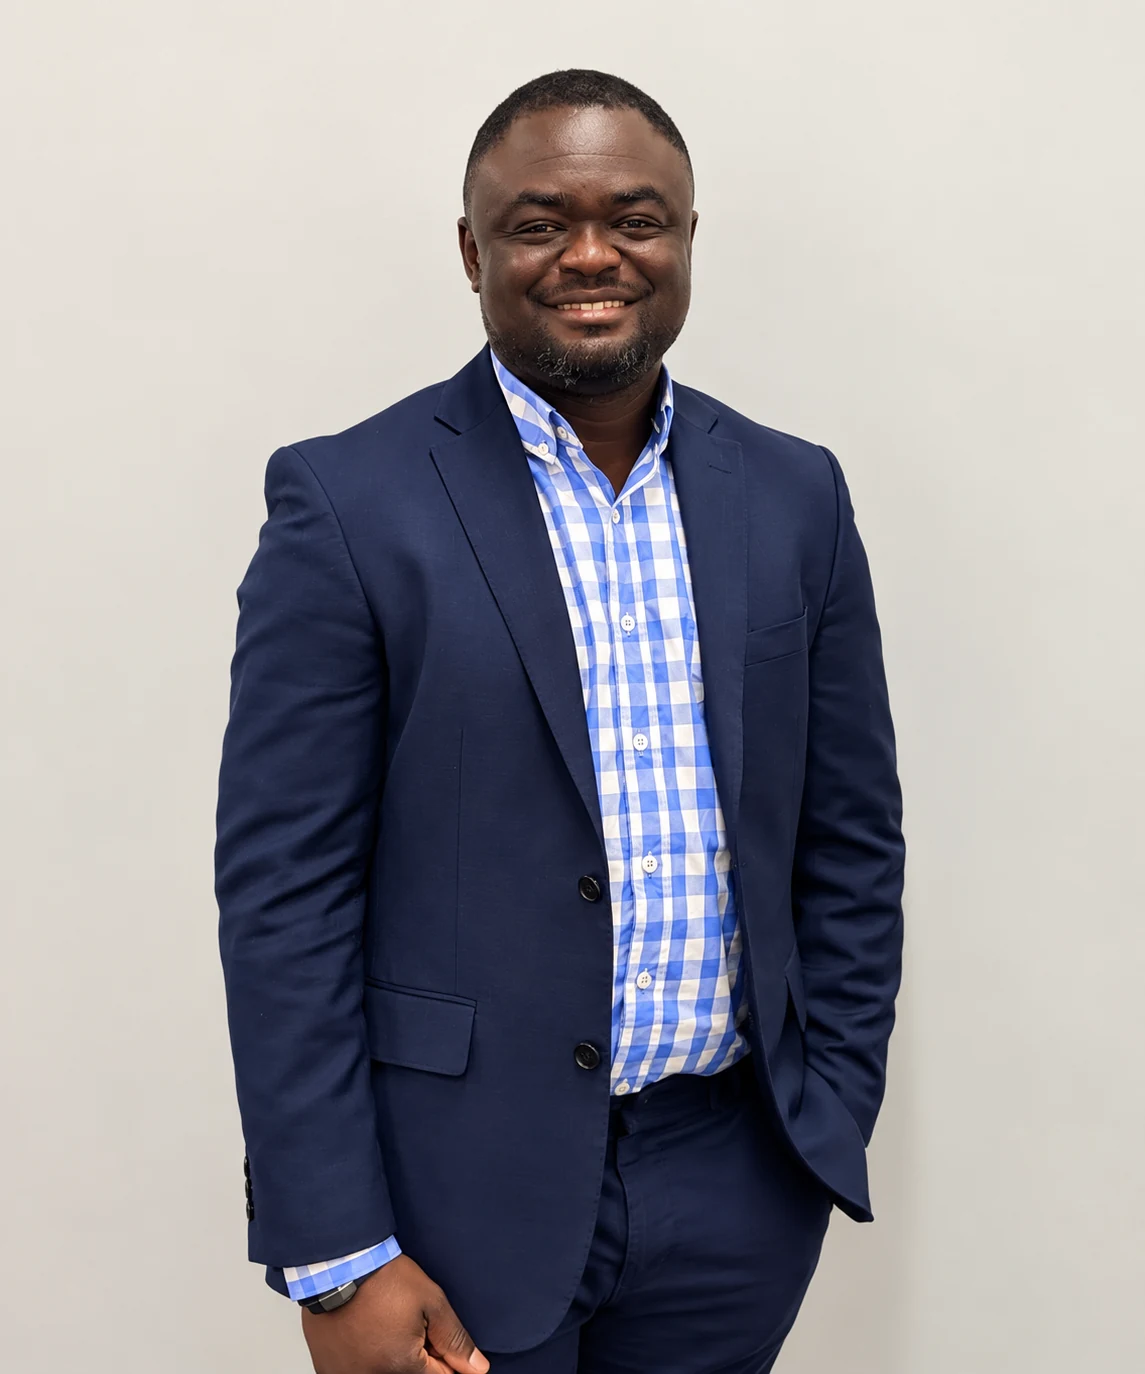
Kenny Vic
Founder & Principal Cybersecurity Consultant
Kenny Vic is a cybersecurity professional with extensive hands-on experience across security operations, security engineering, vulnerability management, identity and access management, privileged access management, data protection, endpoint security, security monitoring and governance, risk and compliance.
His experience includes practical implementation, assessment, auditing and compliance work across security frameworks and programs, including ISO/IEC 27001 and PCI DSS.
Kenny's approach combines technical security experience with practical communication. Through The Cyber Guy, he explains cybersecurity using simple, real-world examples so that business owners, employees and everyday technology users can understand what the risks mean and what they can actually do about them.
Kennyvicops was created to take that practical approach from education into professional cybersecurity services.
Practical experience across the disciplines that protect a modern business.
Applied experience with the frameworks that shape business security.
Kennyvicops brings practical experience applying security frameworks, controls and compliance requirements to real-world security environments.
“Experience” is used intentionally. It reflects hands-on work with these frameworks — not certifications, and not an implication that Kennyvicops is a certification body.
Hands-on work with security technologies businesses actually use.
PAM
Vulnerability Management
EDR / Endpoint
SIEM / Monitoring
Data Protection
Cloud
Technology names listed reflect professional experience with these technologies and do not imply partnership, sponsorship, certification, or endorsement.
Straight answers, in plain English.
What type of businesses do you help?+
Small and growing businesses that need practical cybersecurity guidance, and organizations that need additional cybersecurity expertise alongside an existing IT team.
What does a cybersecurity assessment involve?+
A structured review of your environment, current security controls, key risks and business priorities — followed by a prioritized set of practical improvements.
Do small businesses really need cybersecurity services?+
Yes. Smaller businesses are frequent targets precisely because attackers assume defenses are lighter. Practical controls make a measurable difference.
How often should vulnerabilities be assessed?+
Continuously, in some form. The right cadence depends on your environment, exposure and business impact — that's part of what we help define.
Why is MFA important?+
MFA is one of the highest-impact, lowest-cost controls a business can put in place. It significantly reduces the risk of stolen passwords becoming full account takeovers.
What is least privilege?+
It means giving each user and system only the access they truly need to do their job — no more. It limits the damage of a compromised account.
How should a business protect its backups?+
Have them, isolate them, protect them from being modified or deleted by attackers, and — critically — test that you can actually restore from them.
What happens if an employee falls for phishing?+
The impact depends on your controls: MFA, endpoint protection, monitoring and a clear incident reporting path can turn a click into a contained event instead of a breach.
How does cybersecurity awareness training work?+
Regular, practical, relevant training grounded in real-world examples — not a one-off lecture. The goal is a security-aware culture, not a memorized checklist.
Can Kennyvicops work with an existing IT provider?+
Yes. We regularly work alongside internal IT teams and external providers to add security expertise where it's needed.
Do you provide remote cybersecurity consulting?+
Yes. Most of our engagements can be delivered remotely, with on-site work when it adds value.